Monitor and intercept shadow contracts and p-card spend
🏆 Industry Recognition
CAUCUS Featured Solution — Next-Gen IT Procurement Risk & Compliance, VendorVault and IT Procurement Summit.
SIG|ORG "Company to Watch" (2027) — Enterprise Sourcing & Governance Innovation
Sting is a 100% on-prem solution that detects employees agreeing to terms and buying products.
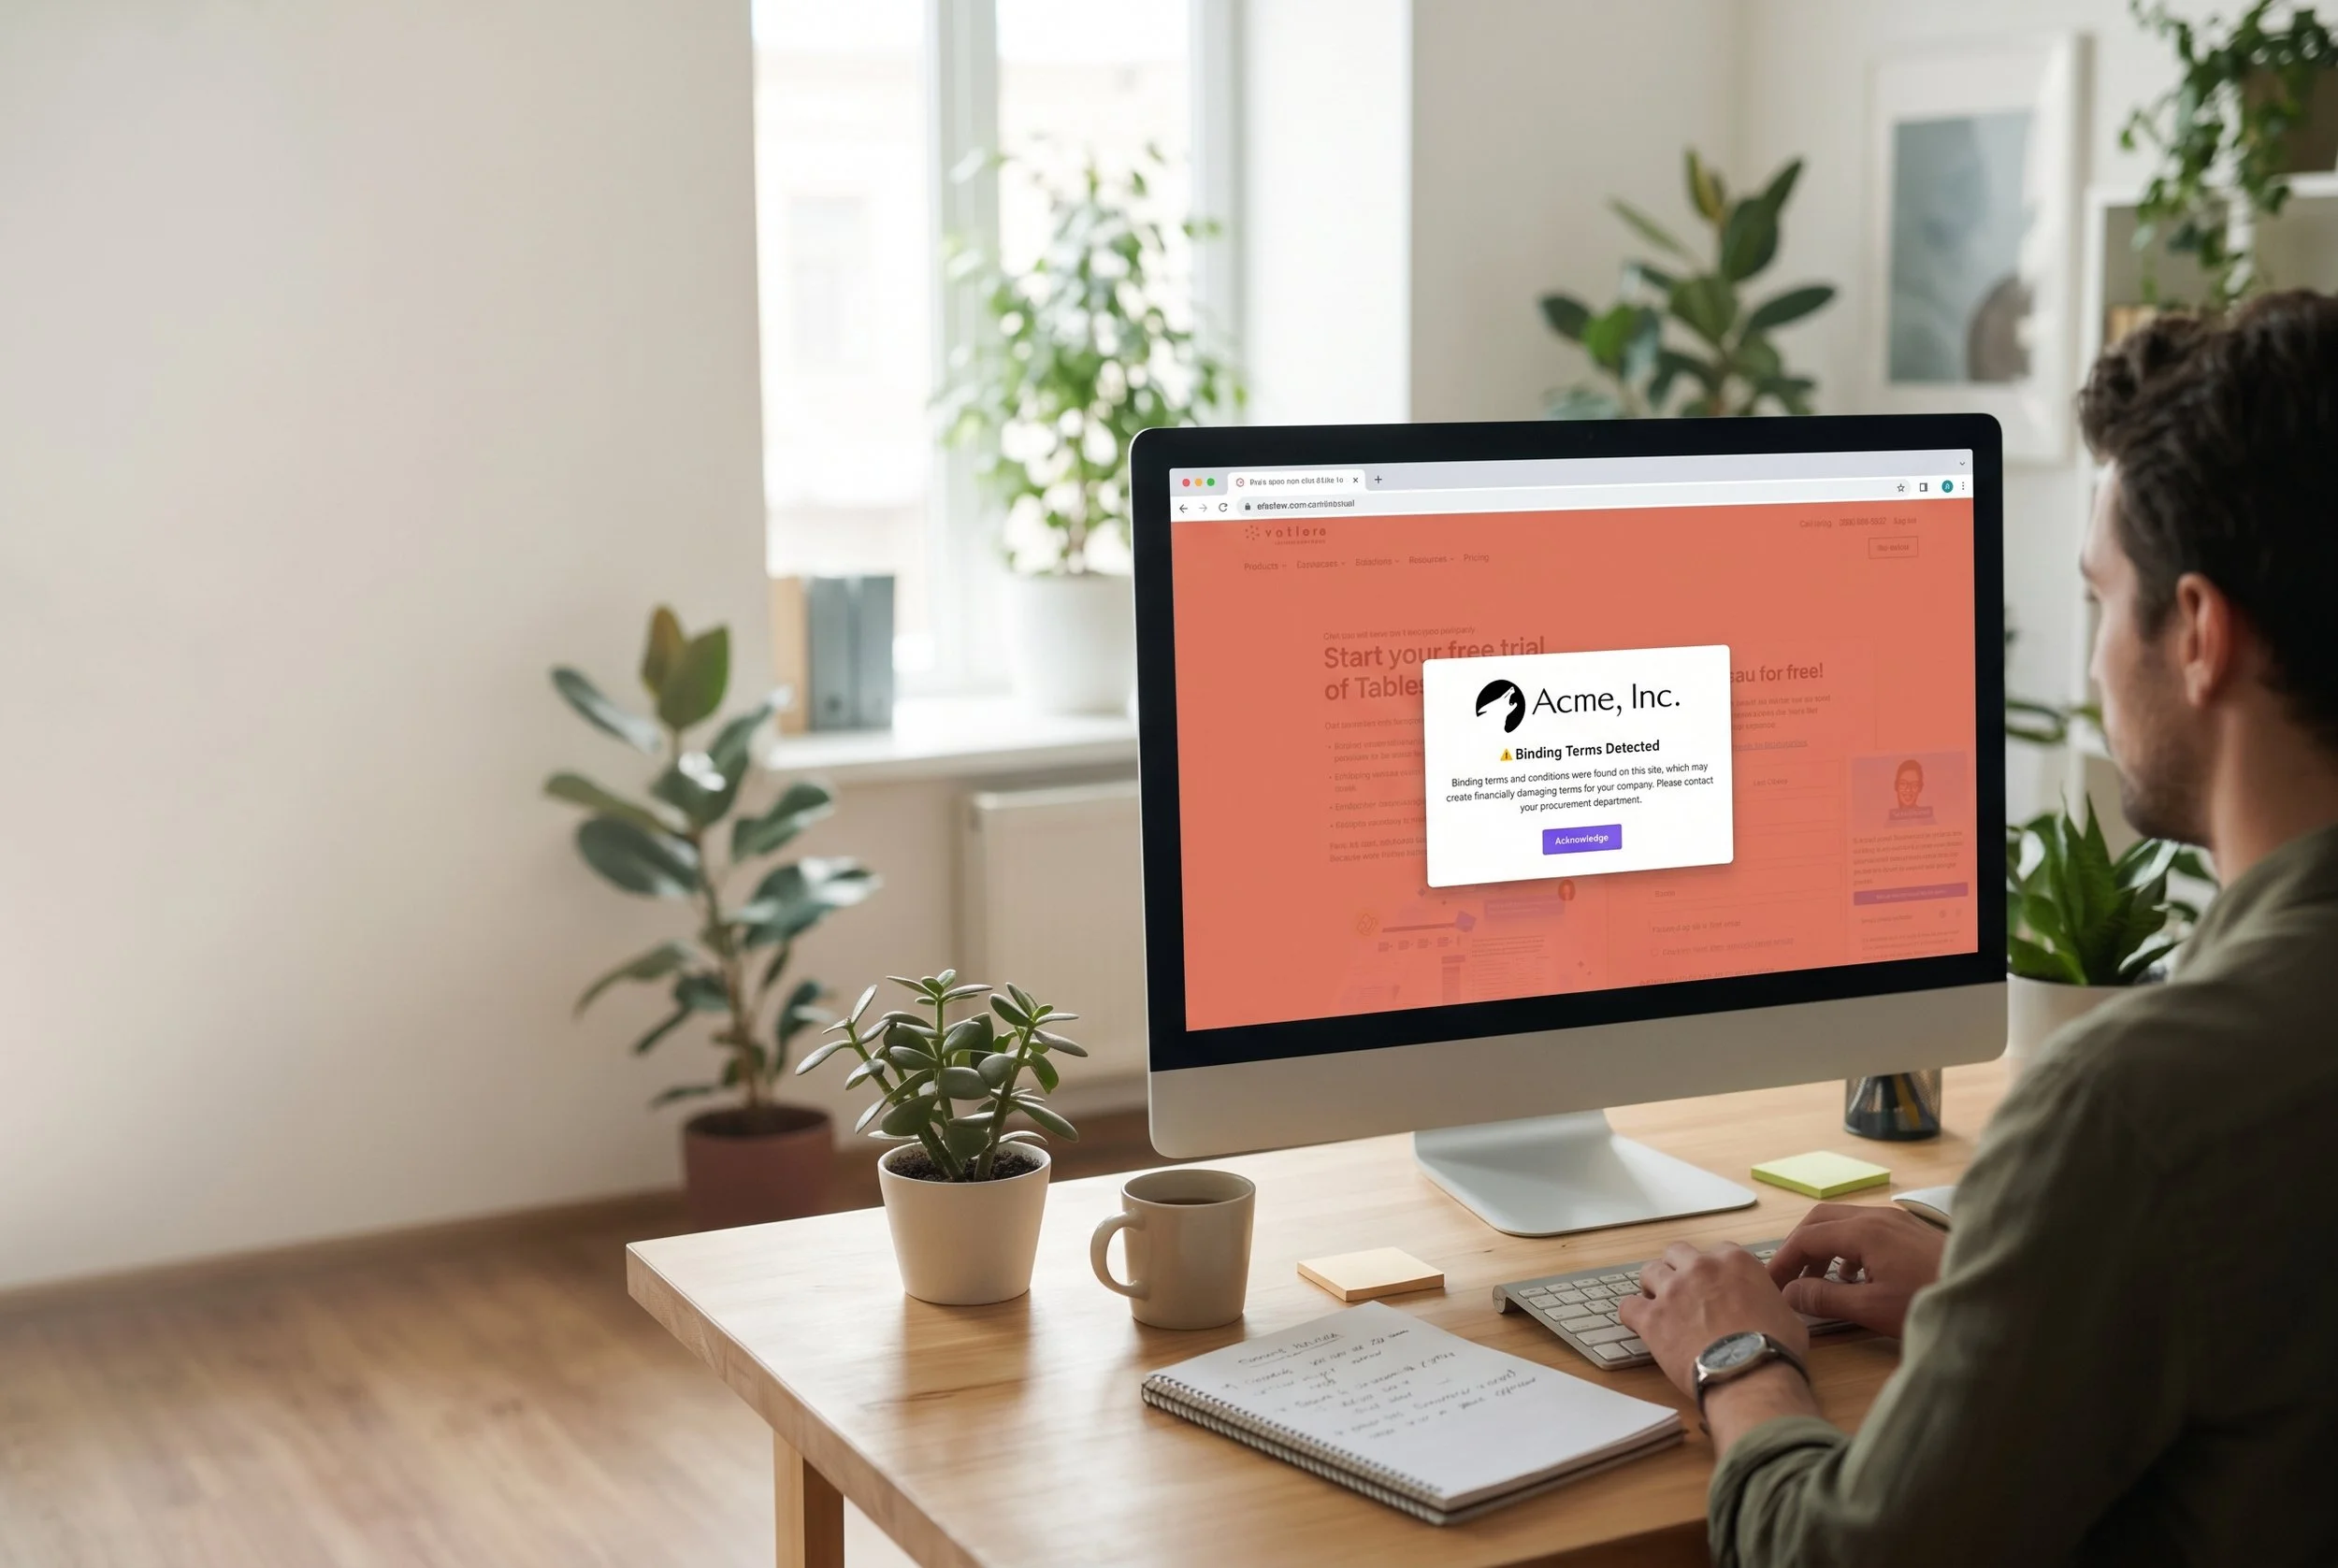
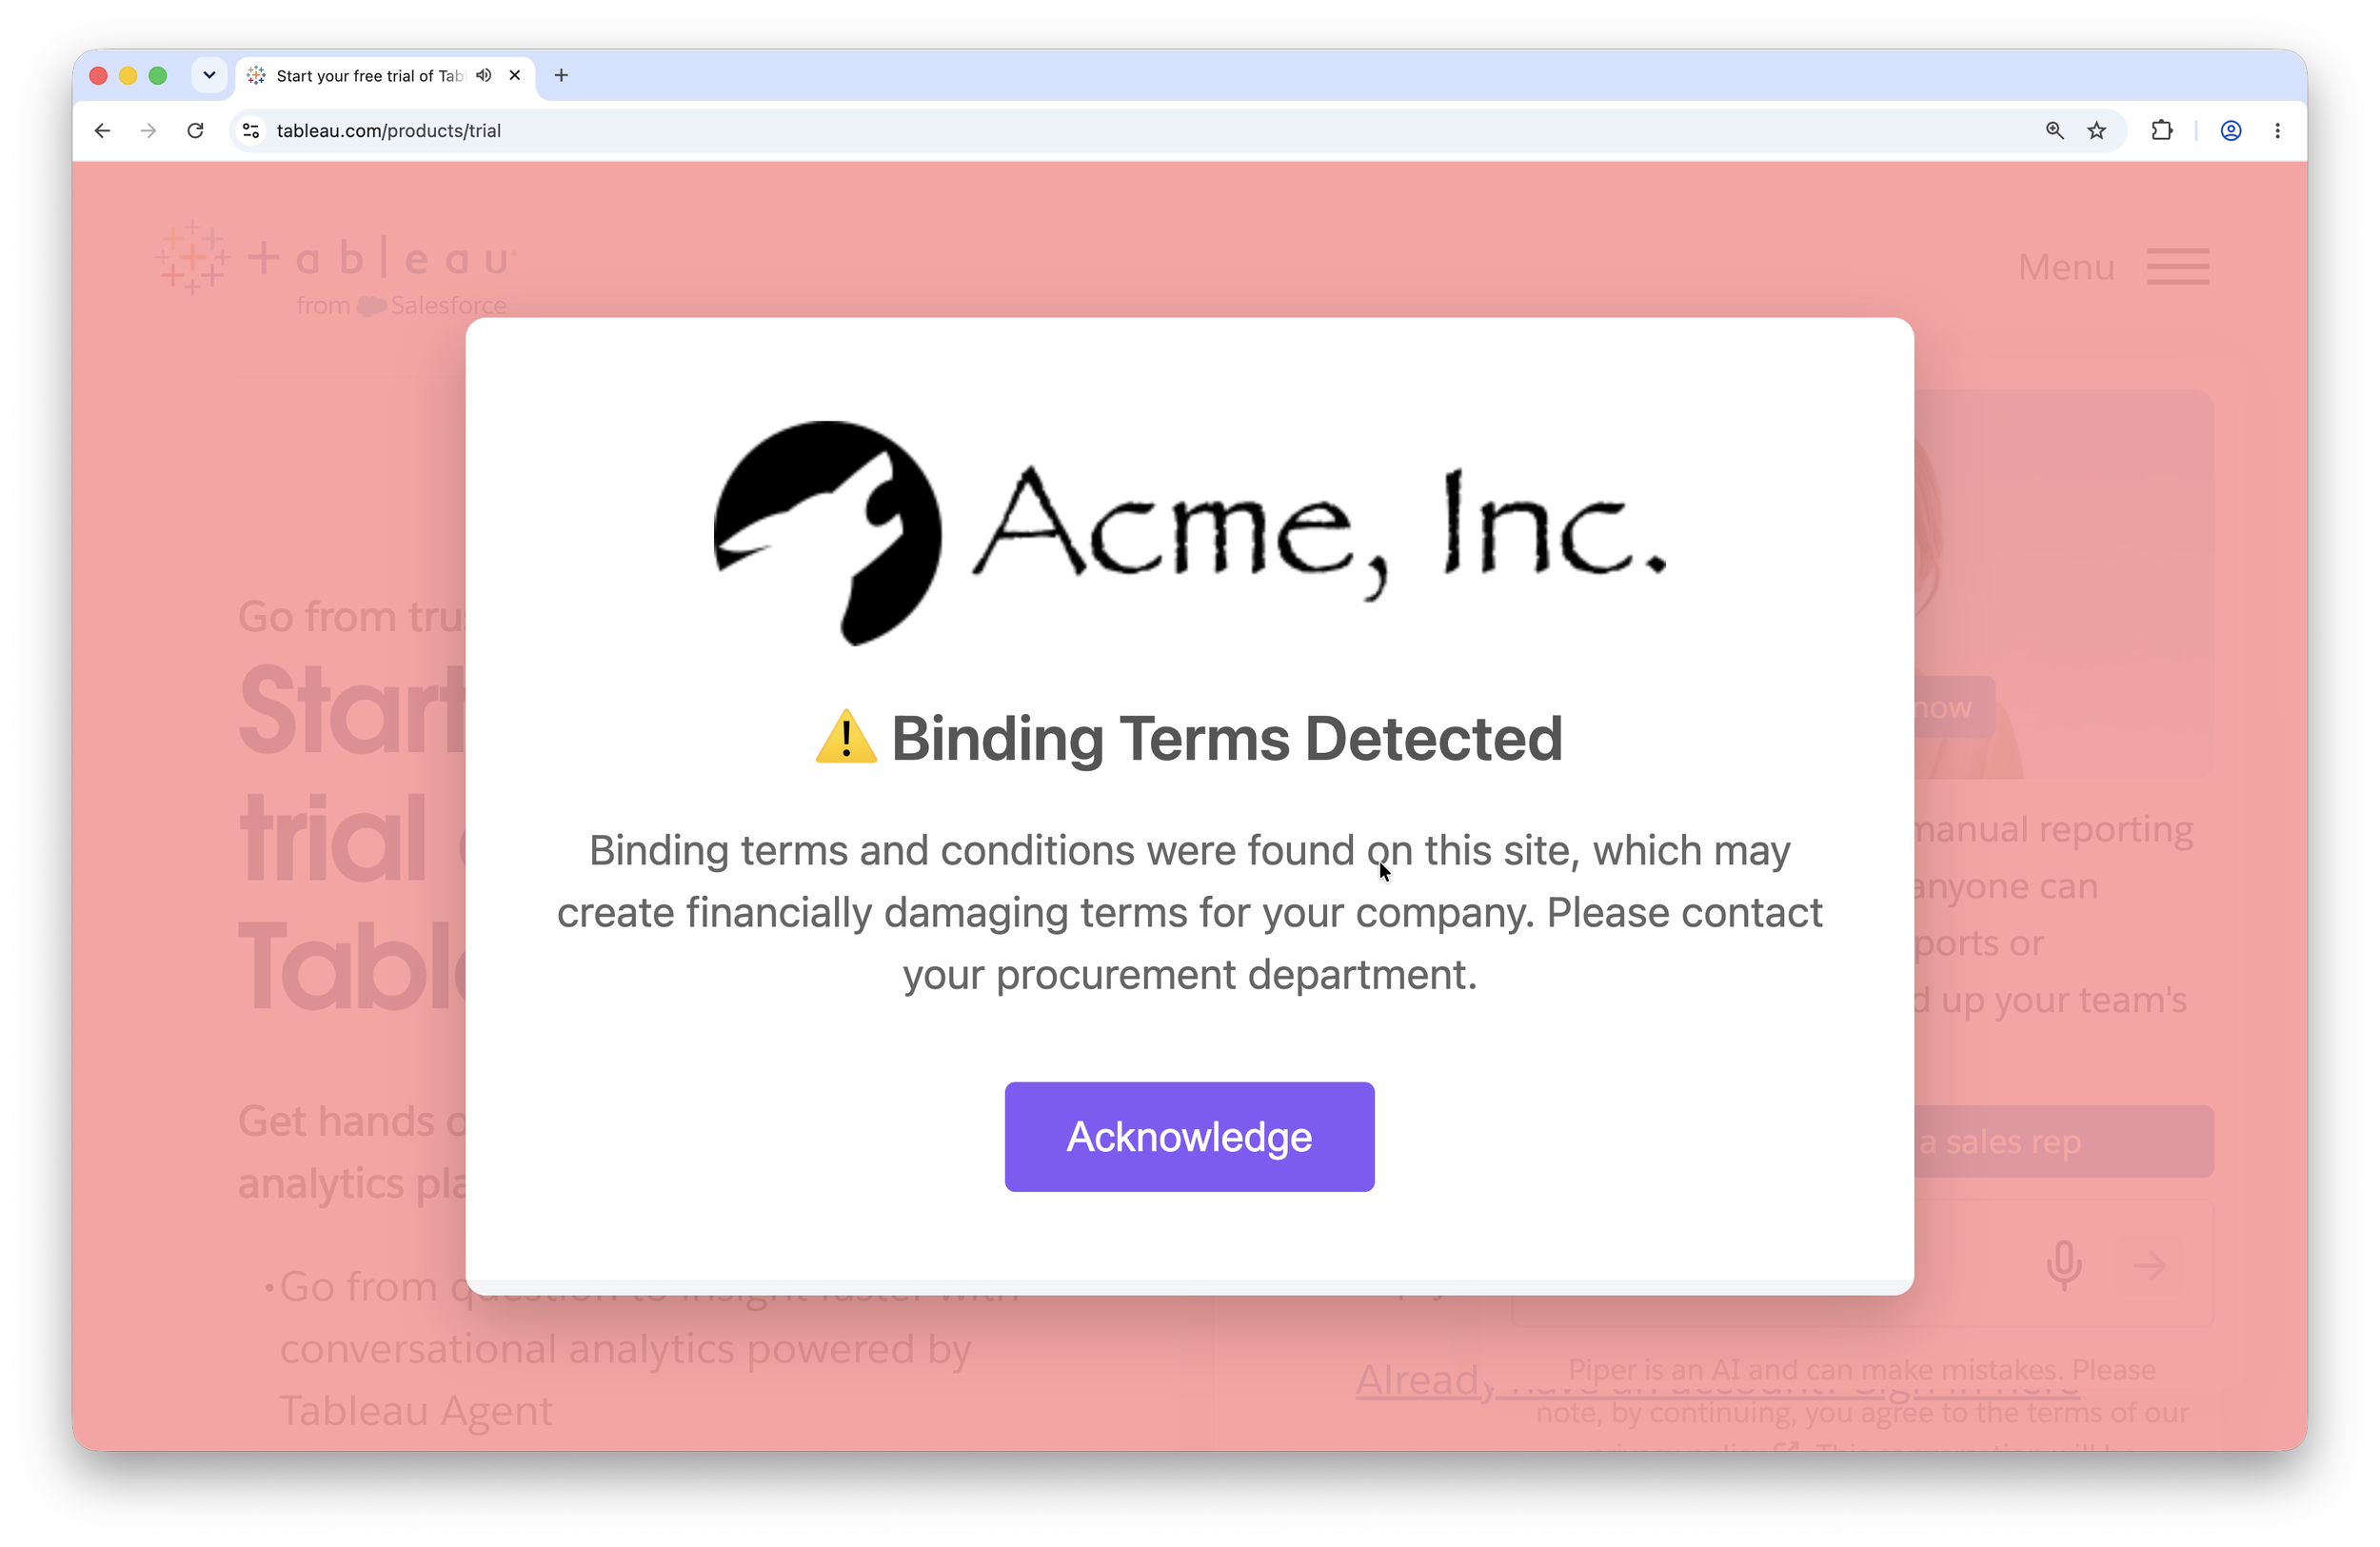
Supports silent monitoring and visual alerts with custom messaging to employees.
Detects legally binding events including clickthroughs, e-signatures, p-cards, and downloads.
Client-side algorithm runs in the safety of web browser sandbox (no cloud, no telemetry, no data collection).
With 99% precision (low false alarms) and 94% recall (low missed alarms), Sting performs above and beyond even with newly launched vendors.
See Sting in Action
What Sting Monitors in Real-Time
01
Shadow Contracts & Unauthorized SaaS
monitor and intervene free trial signups, SaaS tools, and e-signatures.
02
Ad Hoc Auditing
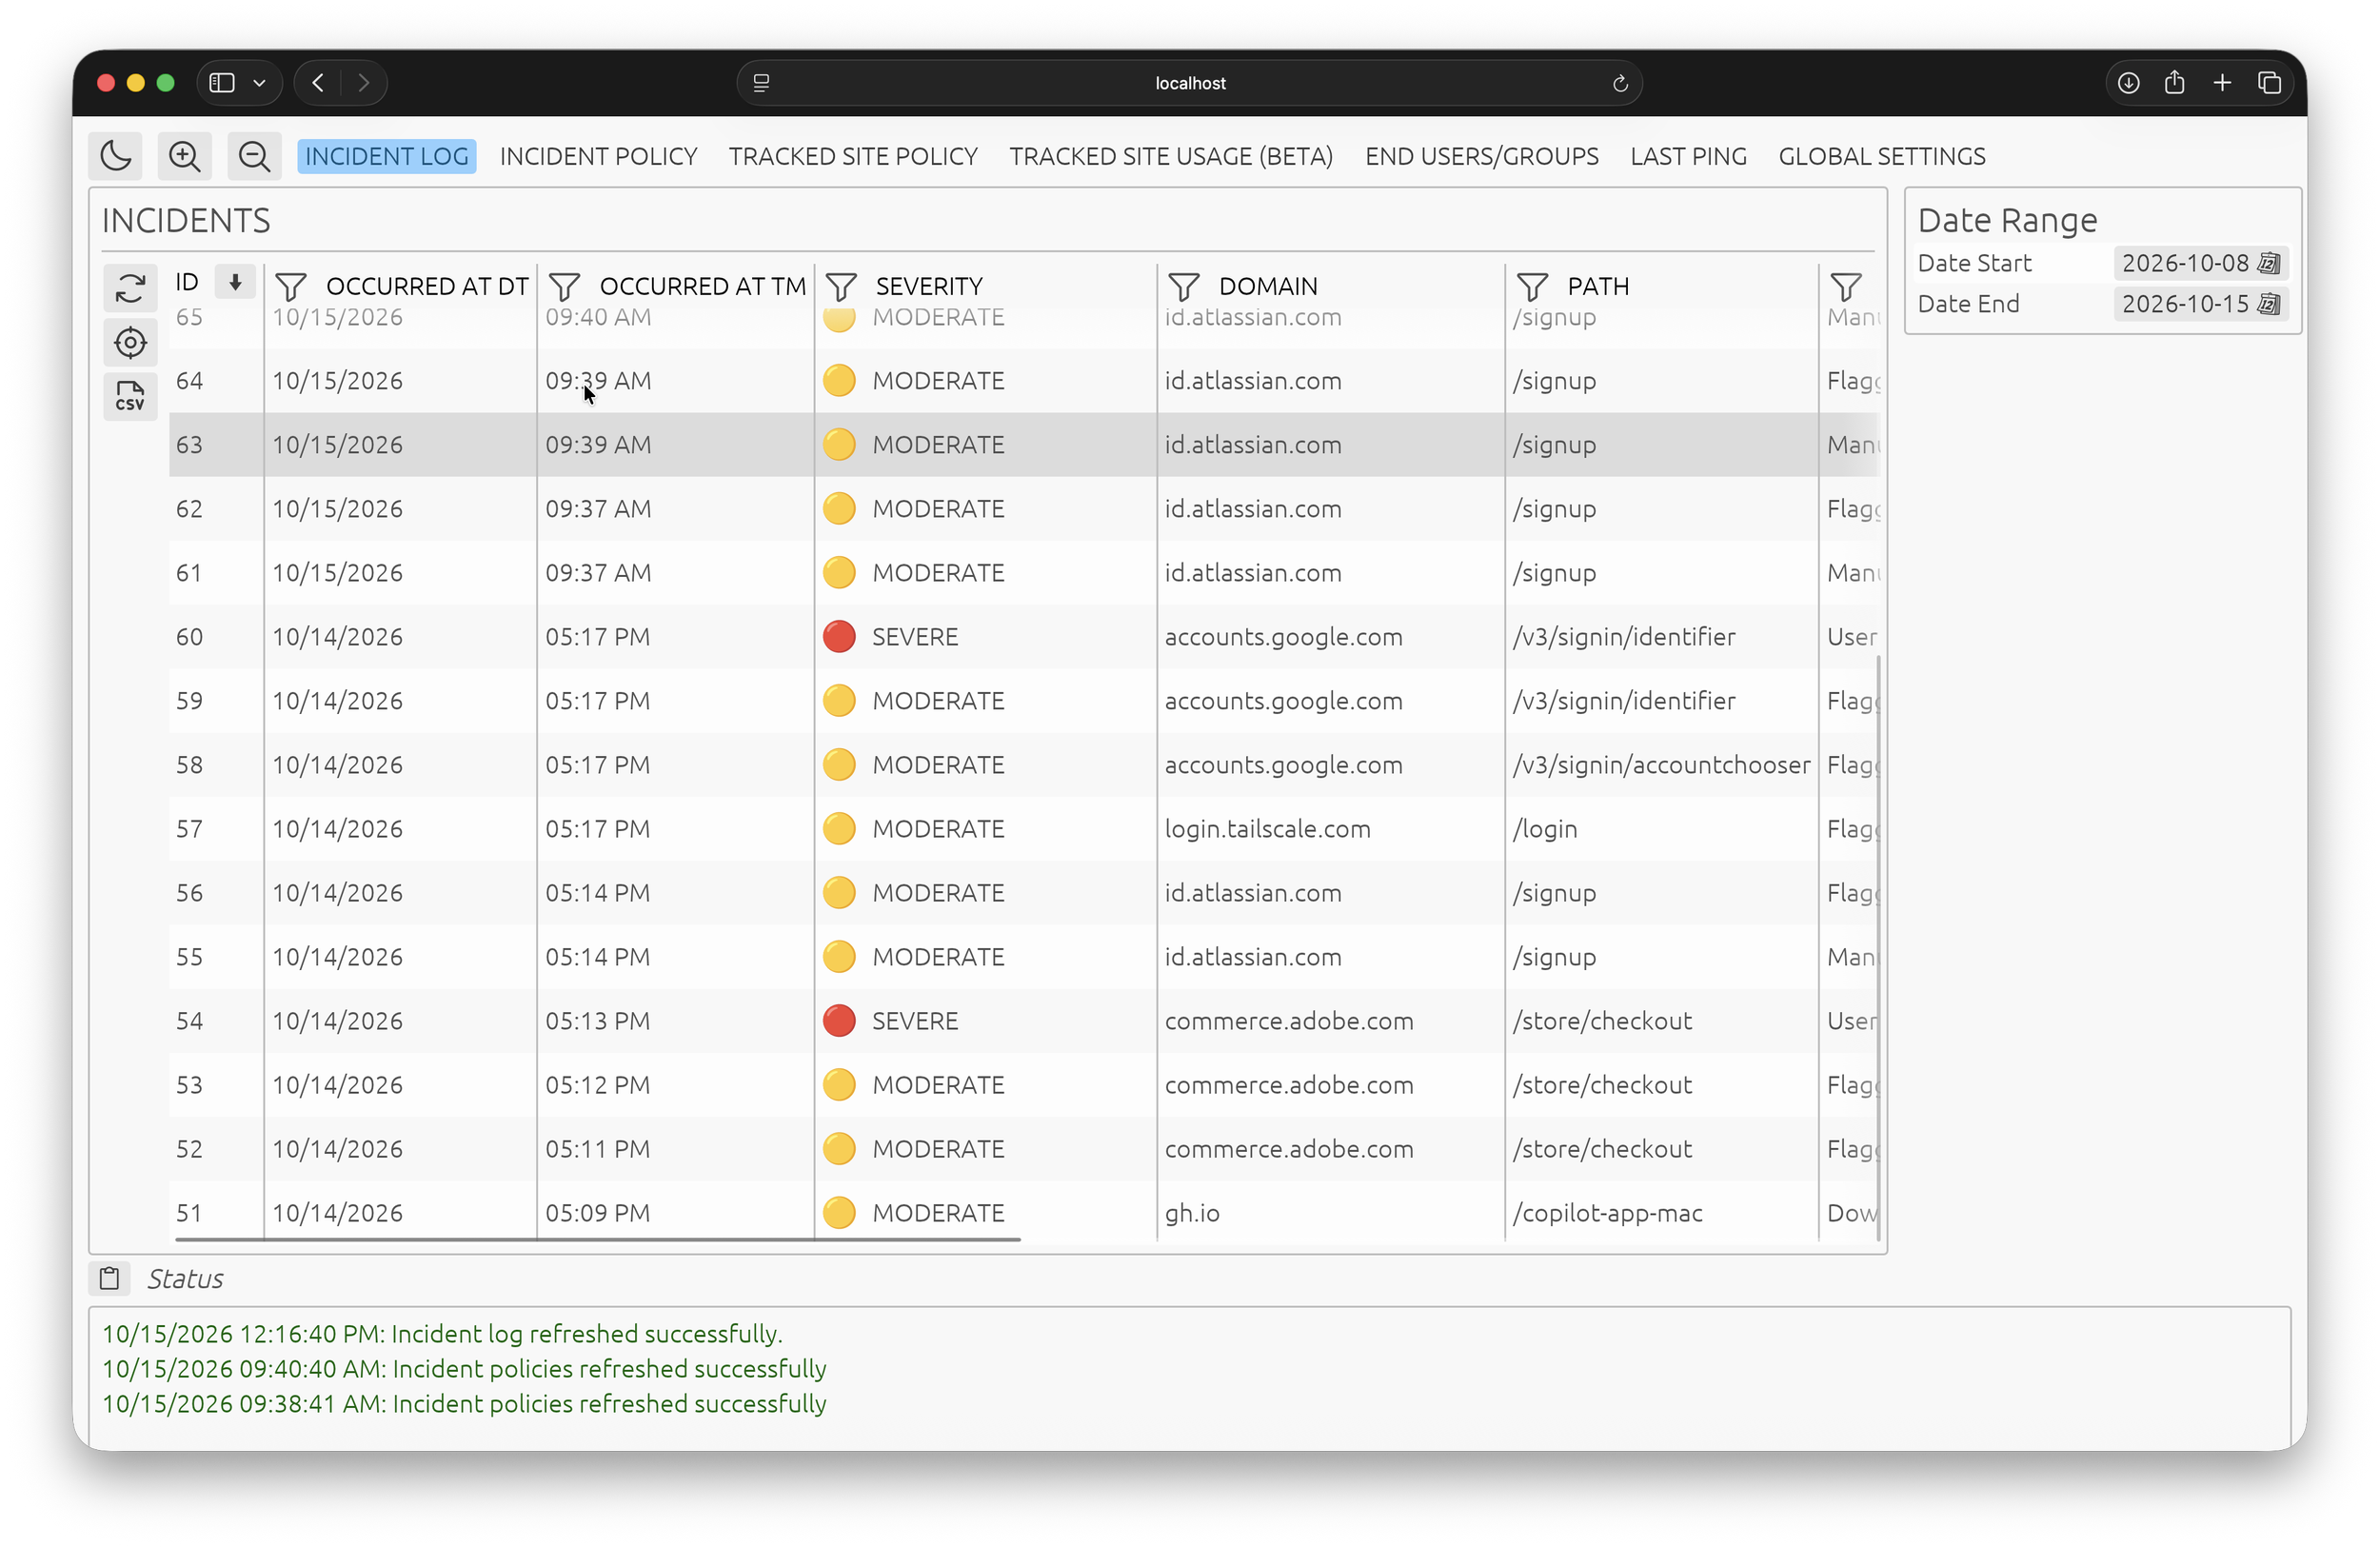
Place custom messaging or tracking on specific sites to detect how often employees are using authorized/unauthorized vendors.
03
Unauthorized P-Card & Rogue Spend
Capture P-Card misuse and unapproved vendor payments.
04
Contract Acceptance
Capture events likely indicating the employee proceeded with a contract or purchase.
Shine a light on Shadow Contracts
Sting is not a vendor management system. It monitors and intercepts real-time binding moments before they become invisible enterprise liabilities, including:
Signups via personal or unmonitored accounts.
Free trial activations with buried clickwrap terms.
Direct transactions with unmanaged, unknown vendors.
Amount of time spent on vendor sites
Sting illuminates shadow activity at the browser edge before contracts bypass legal and procurement oversight.
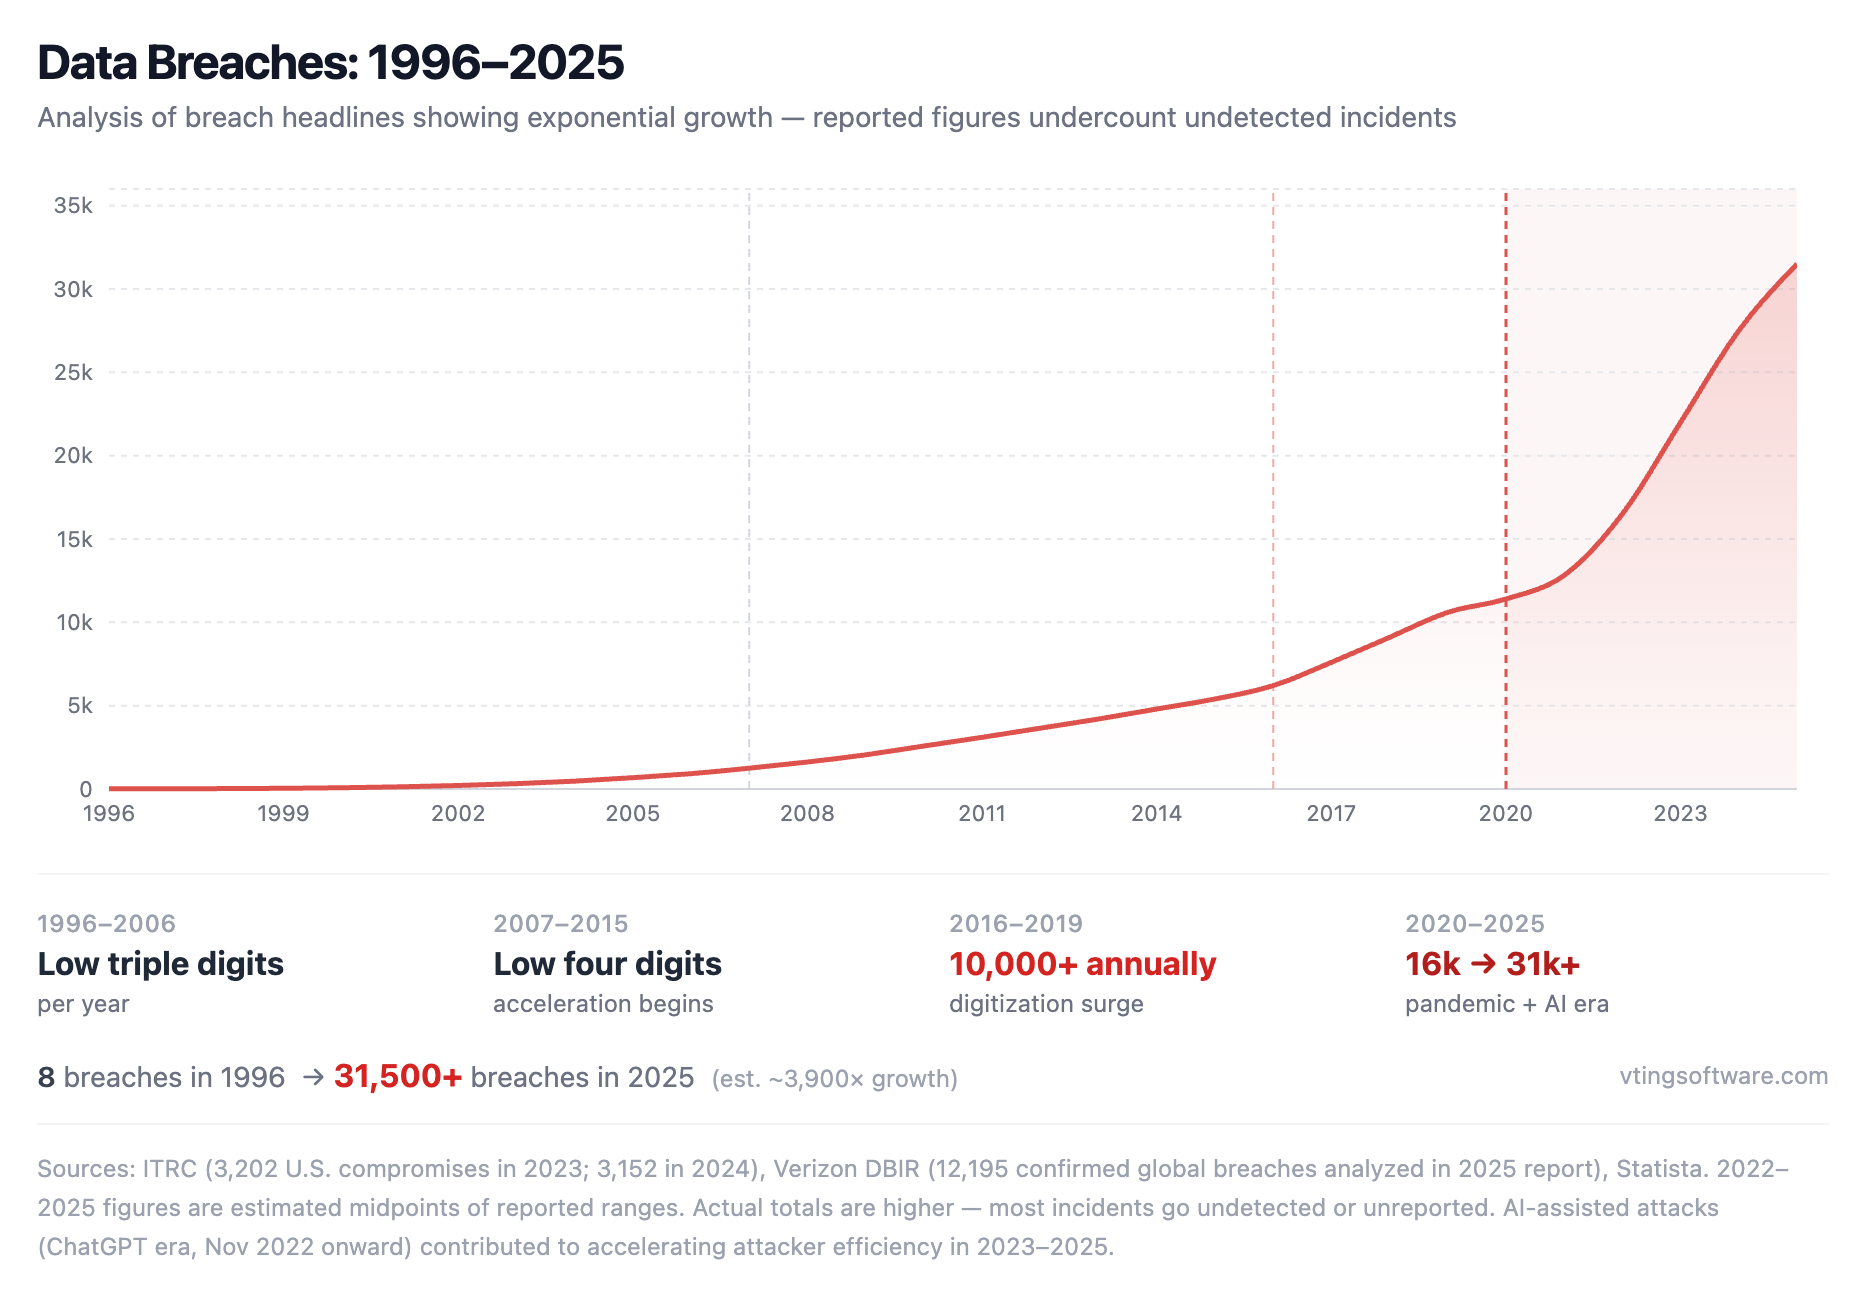
The Threat is Growing